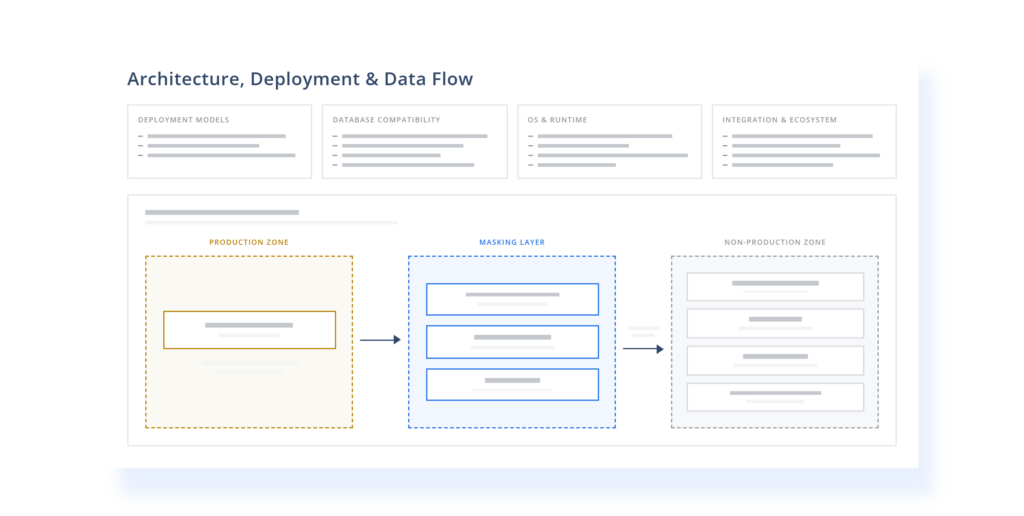
From architectural pressure to regulatory obligation.
When identity becomes the perimeter, the compliance boundary moves with it. We map which controls your regulations require across DORA, NIS 2, HIPAA, PCI DSS, NERC CIP, 800-53, CSF, ISO 27001, and MITRE, so your architecture decisions carry their regulatory evidence with them.
EVALUATE
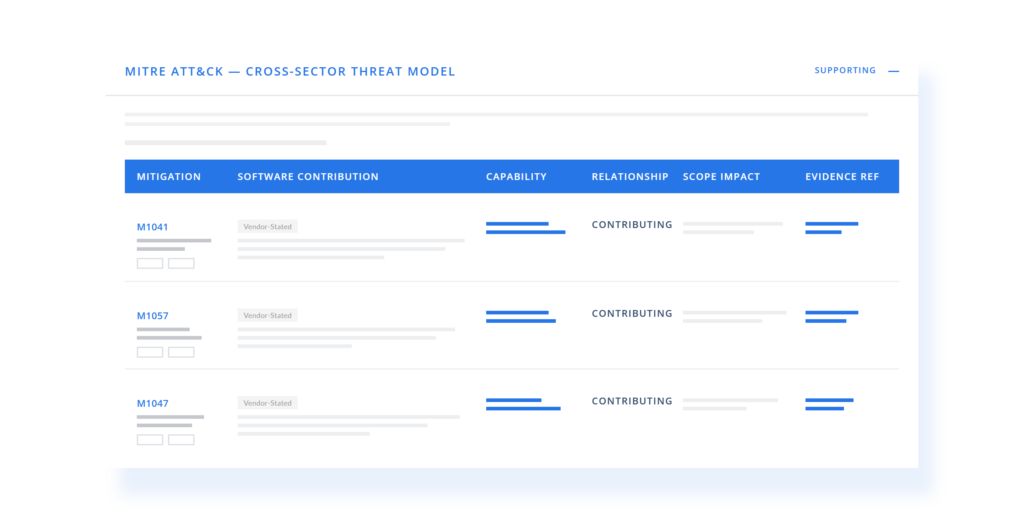
MITRE ATT&CK coverage analysis across attack surfaces
AI and software security tools evaluated across MITRE ATT&CK for Enterprise, ICS, and Mobile, and MITRE ATLAS. See exactly which mitigations a product enforces and which architectural gaps remain. Threat coverage data your zero trust roadmap, identity strategy, and OT segmentation decisions can actually be built on.
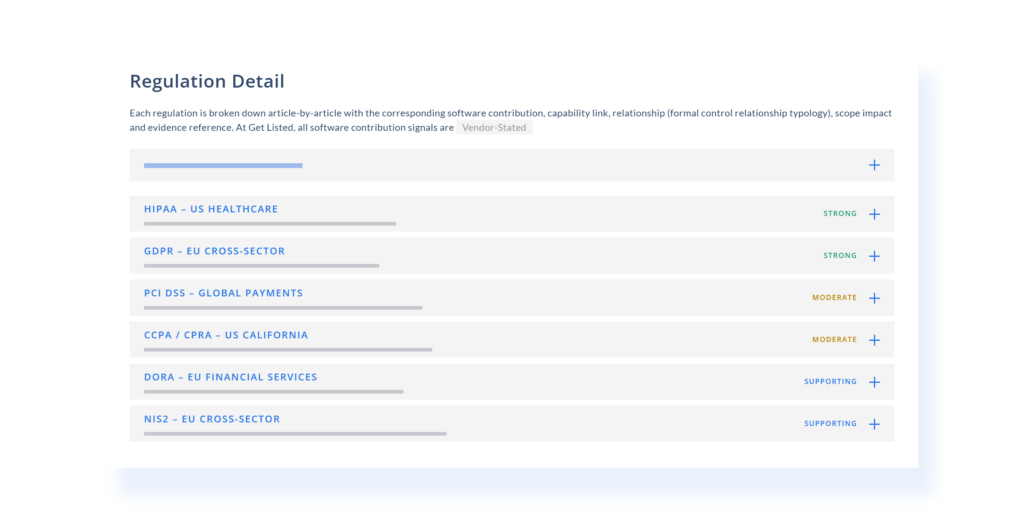
Multi-framework comparison for cross-regulation architectures
Compare how the same product addresses DORA Art. 9, NIS 2 Art. 21, HIPAA Security Rule, and PCI DSS Req. 6 at once. Identify where a single architectural decision satisfies multiple obligations and where regulations conflict in practice. Designed for architects working across jurisdictions and frameworks, with a dedicated Compliance Labs analyst on complex engagements.
Compliance mapping built for security architects
The expertise behind every compliance map and report.
Independent evaluations
Vendor-neutral assessments designed for architects validating software before deployment.
IT, OT & AI Expertise
Supporting security architects across IT, OT and AI environments since 2000.
Built by Practitioners
Designed by compliance officers who map regulatory controls to real-world architectures.
Contact us today
We are here to help you find the right software solutions to grow your business and achieve your goals.
Select the fields to be shown. Others will be hidden. Drag and drop to rearrange the order.